
Nefarious North Korean Cyber Activity
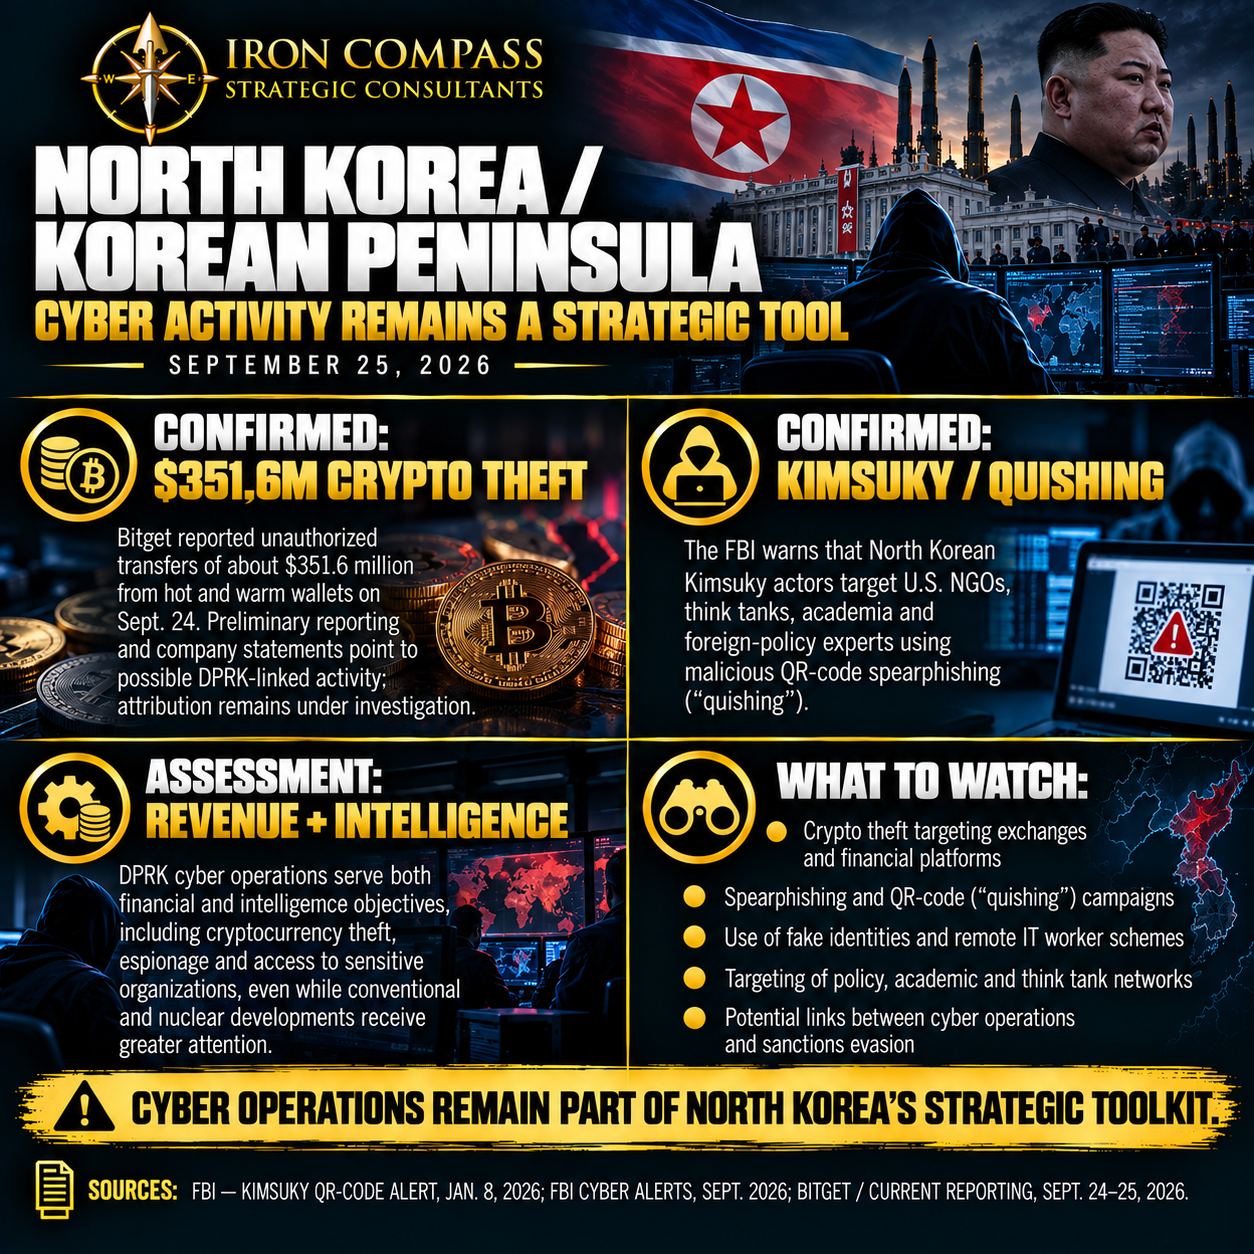
NORTH KOREA: CYBER OPERATIONS REMAIN A STRATEGIC TOOL
North Korean cyber activity continues to operate across both financial and intelligence targets. On September 24, cryptocurrency exchange Bitget reported unauthorized transfers affecting approximately $351.6 million in digital assets. Bitget’s CEO said preliminary findings showed similarities to known North Korean operations, but the attacker’s identity remains under investigation.
The financial dimension is only part of the threat. In January 2026, the Federal Bureau of Investigation (FBI) warned that North Korean Kimsuky actors were targeting U.S. Nongovernmental Organizations (NGO), think tanks, academic institutions and foreign-policy experts using malicious QR-code spearphishing, or “quishing.” The technique can redirect victims to credential-harvesting pages and potentially enable session-token theft and account compromise.
For organizations, the key issue is exposure rather than simply attribution. Companies and institutions with cryptocurrency assets, sensitive research, foreign-policy work, technology, financial infrastructure or internationally connected personnel should monitor unusual authentication activity, QR-code phishing, impersonation attempts and suspicious access to cloud accounts. North Korean cyber operations demonstrate how cyber activity can simultaneously generate revenue, collect intelligence and create access to sensitive organizations.
SOURCES
TechCrunch — North Korean hackers suspected in $351M crypto theft
September 25, 2026
https://techcrunch.com/2026/09/25/north-korean-hackers-suspected-in-351m-crypto-theft-the-largest-so-far-this-year/
Federal Bureau of Investigation — North Korean Kimsuky Actors Leverage Malicious QR Codes in Spearphishing Campaigns Targeting U.S. Entities
January 8, 2026
https://www.fbi.gov/file-repository/cyber-alerts/north-korean-kimsuky-actors-leverage-malicious-qr.pdf
Federal Bureau of Investigation — North Korean Actors Exploit Weak DMARC Security Policies to Mask Spearphishing Efforts
May 2, 2024
https://www.fbi.gov/file-repository/cyber-alerts/north-korean-actors-exploit-weak-dmarc-security-policies-to-mask-spearphishing-efforts-050224.pdf